The program

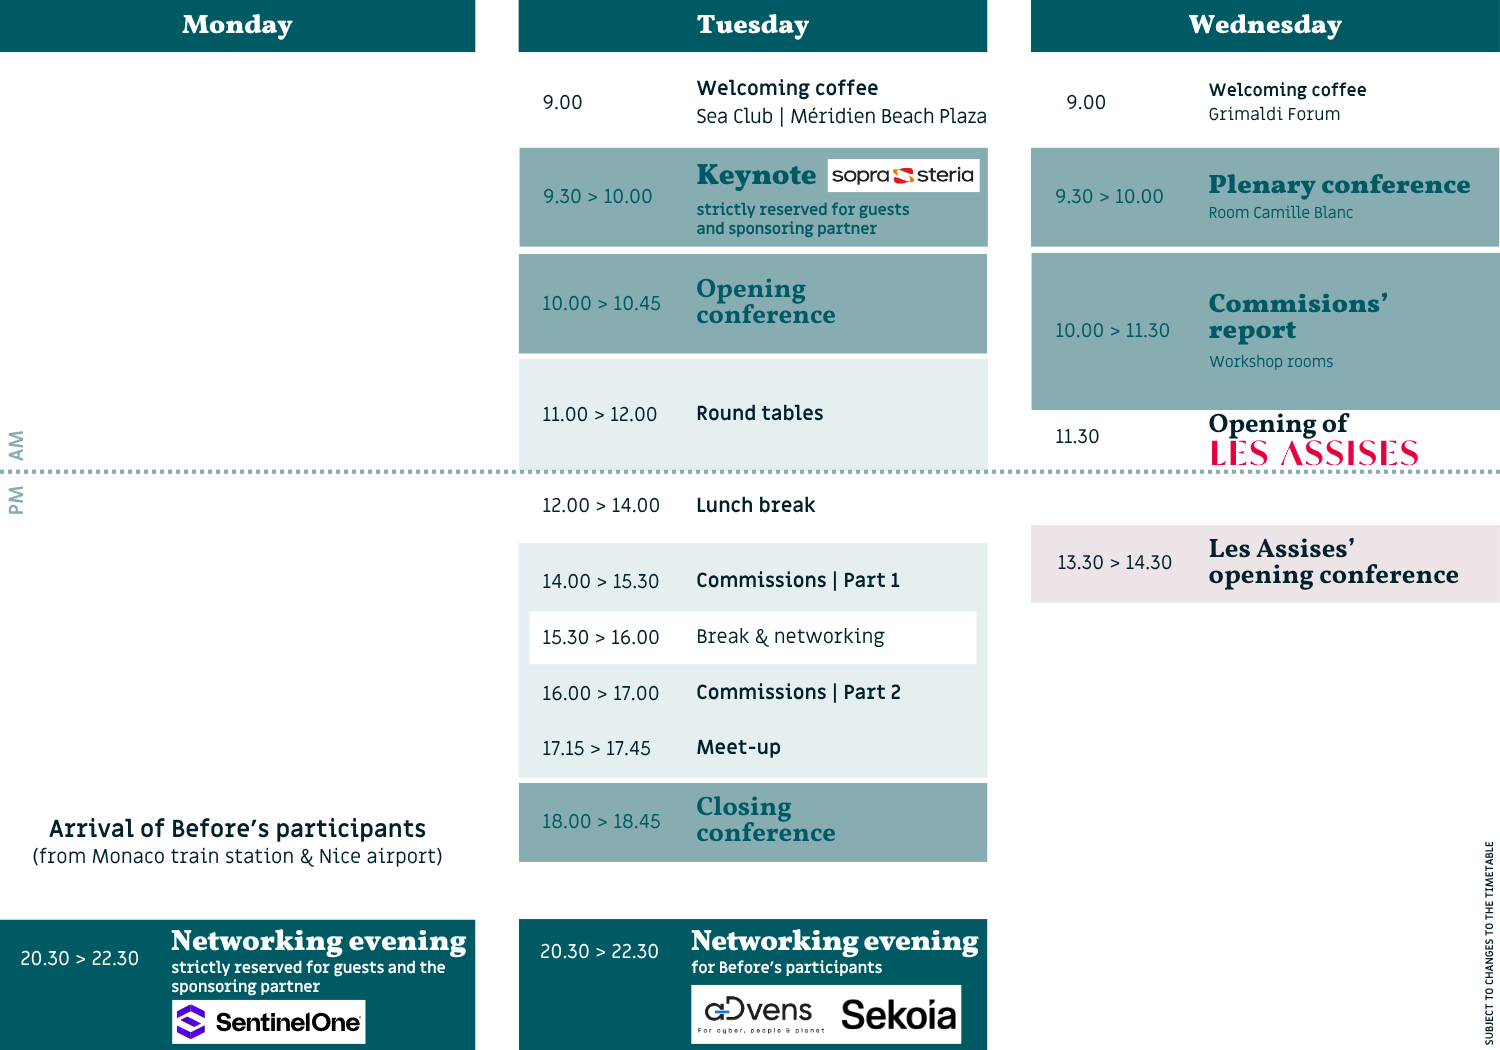
Programme at a glance
Browse the full program for the 2026 edition!
-
Keynote Sopra Steria
As the balance of power shifts on a new scale with AI, should cyber defense change its model, and how should it go about doing so?
AI is no longer just a tool in the cyber arsenal; it is redefining the very scale of risk - to the point of raising questions about critical cyber capabilities for frontier models. For large organizations that are already cyber-mature, the challenge is no longer whether to prepare, but to what extent they should transform their defense models, technology choices, and resilience strategies - in Europe, navigating the balance between a global and a sovereign approach.Speakers:
- Fabien Lecoq, CEO Cybersecurity Business Line Group - Sopra Steria
- Véronique Loquet, Cybersecurity Expert
-
Opening conference
Anticipating Uncertainty: The New Pillars of Cyber Resilience
Today, it is no longer just a question of managing cyber risk, but of preparing our organizations to evolve in an environment where uncertainty becomes the norm.
What major changes should be anticipated in the coming years? How can you evolve your security strategy in the face of threats that now extend beyond the technological framework?
To open the Before 2026, Lieutenant General Aymeric Bonnemaison, Director of Intelligence and Defense Security (DRSD), will share his reading of the major changes in the strategic environment. Through an exchange with Nicolas Arpagian, he will shed light on the evolution of threats, new power dynamics and lessons that organizations can draw from the world of intelligence to strengthen their anticipation, resilience and decision-making capacity.
In the second part, Olivier Caleff, CEO of FIRST, interviewed by Emmanuel Orlando, will share feedback from the largest global community of incident response teams to identify the factors that make a difference: preparation, cooperation, information sharing, skills development and trust.Speakers:
- Fabrice Bru, Director of Cybersecurity - France Travail, and President of CESIN
- Aymeric Bonnemaison, Lieutenant General, Director of Defense Intelligence and Security (DRSD)
- Nicolas Arpagian, VP of Strategy, Jizô AI et Columnist - Les Echos
- Olivier Caleff, President of FIRST, Interim CSIRT Lead - CSIRT.fr
- Emmanuel Orlando, Director Cybersecurity Governance - Dassault Systèmes
-
Commission 1 - National Cybersecurity Strategy: Aligning the Cost of Implementation with the Level of Ambition
The National Cybersecurity Strategy 2030 sets forth a bold vision to strengthen the digital resilience of our organizations, our infrastructure, and our economy. In the face of escalating threats, evolving regulations, and the emergence of major technological disruptions, this vision is essential.
But success cannot be decreed. Between stated ambitions and the reality on the ground, organizations must overcome numerous challenges: governance, skills, engagement of business units, execution capacity, and risk management. How can this strategic vision be transformed into concrete and sustainable actions?
This committee proposes to collectively explore the levers that will make it possible to turn this vision into reality. Through sharing best practices, peer discussions, and collaborative workshops, participants will identify concrete actions to take today to effectively prepare organizations for the cybersecurity challenges of tomorrow.
Speakers:
- Co-Chair: Thierry Auger, Group CISO - Lagardère
- Co-Chair: Olivier Ligneul, Group CISO - EDF
Partner: Antoine Grenier, Head Of Cybersecurity Products - Eviden
Moderator: Annick Rimlinger, Director of Safety, Security, Cyber, and Data Protection - Aéma Groupe
-
Commission 2 - AI and Addictions: How Can We Stay in Control of Our Choices?
Every day, AI is reshaping the balance of power in the cybersecurity market. Recent strategic shifts among major technology players, the rapid advancement of AI platforms, and the emergence of new models of dependency are raising questions about organizations’ ability to retain control over their decisions.
How can we assess the impact of these transformations on cybersecurity strategies? What risks of technological, economic, or operational dependency must be anticipated? How can organizations maintain control over their data, architectures, and long-term strategic direction in an ecosystem undergoing rapid transformation?
This committee aims to provide a broader perspective on the changes underway to help decision-makers decipher market dynamics, inform their investment choices, and strengthen their ability to advise senior management on these issues, which have become strategic in nature.
Speakers:
- Co-Chair: Sébastien Bombal, Director of Technology, Customs - DNRED
- Co-Chair: Patrick Menez, Deputy Group Chief Security Officer - AXA
Partner:
- Gaetan Gesret, Sr Advisory Solution Consultan - ServiceNow Risk & Security
- Pierre-Antoine Failly, Field CTO - Proofpoint
Moderator: Jérôme Saiz, Founder - OPFOR Intelligence
-
Commission 3 - Between innovation and digital resilience, where should we draw the line?
Between innovation, performance, resilience, and digital autonomy, organizations today must balance increasingly complex strategic trade-offs. While adopting new technologies can accelerate their transformation and strengthen their competitive position, it can also create new dependencies and permanently alter their decision-making capabilities.
What compromises are leaders willing to make to balance these imperatives? What criteria enable informed decision-making in an environment where economic, technological, and geopolitical issues are intertwined?
This committee aims to analyze the practices and lessons learned by decision-makers facing these strategic choices. Upon completion of its work, it will formulate concrete recommendations: best practices for executive committees (COMEX) and the teams supporting them in resolving these dilemmas.
Speakers:
- Co-Chair: Florent Kirchner, Director of the Digital Sovereignty Division - General Secretariat for Investment
- Co-Chair: Arnaud Martin, Director of Operational Risks - Caisse des Dépôts Group
Partners:
- Jeremy Bellaiche, Regional Vice President - Spain | Majors Accounts France - Tanium
- Lilian Seigneur, VP Cyber services France - Thales
Moderator: Véronique Loquet, Cybersecurity Expert
-
Commission 4 - Massive Threats: Building Cyber Resilience at Scale
DDoS attacks, ransomware, data breaches, third-party compromises, and large-scale exploitation of vulnerabilities: cyberattacks are growing in scale, speed, and impact.
This panel will analyze emerging trends, recent lessons learned, and French and European initiatives aimed at strengthening collective resilience. It will also provide an opportunity to discuss new models of defense and cooperation in the face of ever-more massive threats.
Objective: to understand how to anticipate, absorb, and respond to large-scale cyberattacks that threaten data, infrastructure, and digital trust.
Speakers:
- Co-Chair: Michel Dubois, Scientific and Technical Director - La Poste Group Cybersecurity Department
- Co-Chair: François Bidondo, SVP Cybersecurity & Infrastructure - SONEPAR
Partner: Raphael Marichez, Chief Security Officer, Europe du Sud - Palo Alto Networks
Moderator: Caroline Moulin-Schwartz, Technical Delegate - CRIP
-
Commission 5 - Geopolitics & Cybersecurity: A New Global Chessboard
Sanctions, extraterritorial laws, regulatory restrictions: geopolitics is now at the heart of a CISO’s scope of responsibility. The real risk is no longer just a cyberattack or the infamous “red button,” but also the possibility that a critical service could be suspended, restricted, or rendered unavailable simply through the application of a legal framework. Legal, financial, and contractual tools are thus becoming new levers of power, with operational and business consequences that are still largely underestimated.
The cases involving the ICC, the Amsterdam Trade Bank, and more recently Mythos and Fable 5 illustrate this shift: without any technical intrusion whatsoever, a compliance decision or regulatory measure can have major effects, serving to shift the balance of power between states.
This committee will bring together peers, under a confidentiality agreement, to collectively produce three concrete and reusable deliverables: a matrix mapping the jurisdictional exposure of critical assets and services; a table of early warning signs and alert thresholds to anticipate rather than react; and a case for the Executive Committee to integrate these issues into the company’s strategy.
The goal: to walk away with a practical approach to integrating geopolitical risk into cyber governance, strengthening the organization’s resilience, and making cybersecurity a recognized driver of performance and sovereignty. A space to share what isn’t discussed in public and compare practices that actually work.
Welcome on board!
Speakers:
- Co-Chair: Jean-Christophe MATHIEU, Global CISO - SNCF Group
- Co-Chair: Emmanuel Garnier, Head of Cybersecurity - Orano
- Christine Dugoin-Clément, Researcher, "Risks" Chair at IAE Paris, AI Observatory at Paris 1 Panthéon-Sorbonne, and AMGN
Partner: Blandine Delaporte, Senior Director, Solutions Engineering - SentinelOne
Moderator: Mélanie Benard-Crozat, Editorial Director - S&D Magazine and Impact for the Future
-
Commission 6 - Dare to Interpret the Threat Differently: From Weak Signals to Strategic Intelligence
The most critical threats are not always the ones we monitor. Cyberspionage, internal threats, disinformation campaigns, the misuse of artificial intelligence, and risks related to the international structure of businesses: these are all issues that often develop in the blind spots of traditional security systems.
In an environment where information is abundant but sometimes difficult to analyze, how can we identify the weak signals that truly warrant attention? How can we account for business-specific factors, local constraints, cultural or regulatory differences between countries, and the potential impacts on the company’s operations?
Through lessons learned and real-world case studies, this panel will explore how to broaden the understanding of threats, transform information into actionable intelligence, and integrate these new risk factors into security decisions. Because anticipating threats today also means looking beyond cyber.
Speakers:
- Co-Chair: Éric Freyssinet, Senior Advisor on Cybercrime & Cybersecurity - COMCYBER-MI
- Co-Chair: Frank Van Caenegem, CISO - Schneider Electric and CESIN Administrator
Partner: Max Charon, Counter Adversary Specialist - Southern Europe, Crowdstrike
Moderator: Garance Mathias, Advocate at the Paris Court of Appeal
-
Find out about the Before 2026 meet-ups sessions
The Board Facing Cyber Risk: Building a New Governance Framework
For a long time, the CISO primarily interacted with the Executive Committee or the Board of Directors to manage a crisis, defend a budget, or explain an incident. Today, this relationship is undergoing a profound transformation. Driven by rising risks, new regulations, and the growing accountability of executives, cybersecurity is becoming a permanent fixture in governance bodies.
Some organizations are taking it a step further by creating cybersecurity committees or dedicated forums for dialogue between board members and cybersecurity leaders, with the aim of establishing a regular, informed, and strategic dialogue that goes far beyond crisis management.
Through a cross-exchange of experiences, this meet-up will explore new forms of collaboration between CISOs and boards: how to build a relationship of trust, foster a shared risk culture, and support the transformation of cybersecurity governance within organizations.
Speakers:
- Frank Van Caenegem, CISO - Schneider Electric and Board Member of CESIN
- Estelle Tchigique-Boyer, Group CISO - CNP Assurances
- Maria-Noelle Brisson, Co-founder - CyberReady
Moderator: Eric Domage, Senior Analyst - PAC
Winter Is Coming: 3 Scenarios to Prepare for 2027
As we approach 2027, a year that promises to be decisive, marked by elections, geopolitical and economic tensions, and an escalation of cyber threats, how can we prepare for what might lie ahead?
Join us alongside leaders with strong strategic vision for a forward-looking, interactive meet-up to collaboratively develop three scenarios for the coming winter and understand what to expect. What signals should we watch for? What risks should we anticipate? What decisions should we make now to be ready for tomorrow?
No predictions, just a shared goal: to better equip our organizations to face the unpredictable.
Speakers:
- Axel Castadot, National Director of Information Systems Crisis Management – SNCF
- Sébastien Blard, Head of Cybersecurity – Renault Group
-
Closing Conference - What's Under the Hood of Cybersecurity
To wrap up the Before event, get a sneak peek at the first documentary from the Assises: an immersive journey into three worlds where cybersecurity plays out far beyond the screen.
- COMCYBER-MI tracks down attackers.
- BZ Hunt uncovers vulnerabilities.
- The SNCF rises to the challenge when the cyber world collides with reality.
Three fields, three perspectives, three ways of confronting an ever-evolving threat.
And because a documentary is also told through the stories of those who lived through it, the screening will be followed by an exclusive interview with the participants, offering a behind-the-scenes look at the filming, their realities on the ground, and the lessons they’ve learned.
Speakers:
- Fabrice Bru, Director of Cybersecurity - France Travail, and President of CESIN
- Patrick Touak, Head of the Ministry of the Interior's Cyberspace Command
- Jean-Sylvain Chavanne, CEO de BZHunt
-
Plenary Session - Decision-Making Under Pressure: Protect Your Human Firewall
A cyberattack targets information systems. Stress, on the other hand, targets decision-makers.
When the pressure mounts, our nervous system can be “hacked”: cognitive biases, loss of clarity, slower decision-making, and poor coordination within the crisis response team.
In this experiential workshop, Bruce Hoang will demonstrate how to use simple physiological regulation techniques to quickly restore cognitive availability, improve decision-making, and maintain effective leadership when every minute counts.
Because cyber resilience doesn’t depend solely on the robustness of infrastructure. It also depends on the ability of men and women to remain clear-headed under pressure.
Speaker:
- Bruce Hoang, Co-author of the book "The Power of Movement" - Founder of InMootion